17 Year-Old Teen Says a DMV Mistake and a Fake Seller Cost Him $58,000 in College Savings After His Car Was Repossessed

Car Being Towed


A 17-year-old high school senior in Los Angeles says a car deal he checked from every angle still cost him his college savings — $58,000 he had saved over four years — after the car was repossessed over a lien nobody told him existed. Now he is seeking answers from Carvana and the DMV, and his story is a warning for anyone buying a used car from a private seller.

Arrod Berjis, who enjoys working on vehicles, found a 2019 Mercedes-Benz C63 AMG listed on Autotrader. The price was $58,000, which he believed was under market value, and the plan made sense to him: repair the car, enjoy it, then sell it for a profit and add the money to his college fund. Before handing over payment, he did what careful buyers are told to do — he went to the DMV with the seller to verify the title was legitimate.

An Online Deal That Looked Legitimate

According to Berjis, a DMV clerk told him multiple times that there was no lien on the vehicle and that everything was clear. The title he received from the DMV listed no lien holder, and neither did the Carfax report he obtained. With those two checks coming back clean, he completed the purchase and spent the next three months repairing the car.

The plan was working. After three months of work, Berjis said he had lined up a potential buyer willing to pay $75,000 — a $17,000 profit over what he paid, money earmarked for college. Then, the night before the planned sale, the car disappeared.

The Car Vanished

Believing the car had been stolen, Berjis contacted the Los Angeles Police Department. Officers directed him to a towing company, where he learned the truth: the vehicle had not been stolen at all. It had been repossessed. According to Berjis, the tow company told him, "We were ordered to take this car by Carvana."

That is where the clean title story fell apart. A lienholder — Carvana, in this account — still had a claim on the car, even though no lien appeared on the DMV title or the Carfax report Berjis had checked. Three months after he bought the car, both the money and the car were gone.

The DMV's Answer: The Paperwork was "Overlooked"

When Berjis returned to the DMV seeking answers, he said the original title was taken from him. What a DMV representative told him, in his account, was that sometimes when a title is transferred, the previous paperwork can be overlooked — a lien can be released, and a DMV title can be issued to a buyer, but that title is void and invalid because of the mistake. Berjis summed up the explanation himself: "Mistake or potentially fraud."

That distinction matters, and it is unresolved. The DMV declined to comment because the matter is an open investigation, and Carvana had not responded to requests for comment at the time of the report. Nothing here is proven about what happened inside the DMV or at Carvana — what is documented is Berjis's account, the repossession, and the two institutions' silence so far.

LA has a 'Fake Seller' Problem

The LAPD is investigating, but Berjis said the case has a built-in dead end: the seller's identity and documents ultimately turned out to be fake, which limits what investigators can do. That is the classic shape of a title scam — a seller who does not really exist, paperwork that looks real enough to pass a routine check, and a buyer left holding the loss when the real lienholder comes to collect.

Berjis said his hope now is straightforward: Carvana will either return the vehicle or compensate him for the $58,000 he lost. Without that money, he fears his college plans will be delayed. "It was a big amount of money that I had saved up over the last four years of high school, which was, you know, all meant to go to the goal of going to college, and so that was the end game for it and it will definitely delay that and hold it back," he said.

How to Protect Yourself From a Title Scam

Berjis did more checking than most buyers do, and it still was not enough — which is exactly why this case is worth learning from. Here is what scam watchers recommend before you pay for a used car from a private seller.

First, do not rely on a single title document. Check the title, a vehicle history report, and the state DMV or lien records independently, and be suspicious if anything does not match. A freshly transferred title deserves extra scrutiny, since this case shows a transfer can apparently wash a lien off the paper without clearing it in reality. Second, verify the seller, not just the car: match the seller's government ID to the name on the title, and be wary if the seller rushes you, refuses to meet at the DMV, or cannot produce consistent paperwork. Third, treat an under-market price as a yellow flag, not a bargain — scammers price cars to make buyers move fast and skip checks. Fourth, pay through a traceable method and get a signed bill of sale with the VIN, price, seller's full name, and the statement that the title is lien-free. And if you have already been scammed, report it to local police, your state DMV's investigations unit, the FTC, and the FBI's Internet Crime Complaint Center, and keep every document, message, and receipt.

The hardest lesson in this story is that even the official check can fail. Berjis went to the DMV with the seller and was told repeatedly that everything was clear. If a deal involves a recently transferred title, a seller you cannot fully verify, or a price that seems too good, slow down and get a second, independent check before the money moves. A few extra days of verification is cheap compared to $58,000 and a college fund.

As of the report, the DMV has not commented beyond citing its open investigation, Carvana has not responded, and the LAPD investigation continues. Berjis is still waiting for the car or the money — and for an answer about how a title the DMV itself issued could turn out to be void.

Thief Caught With 350 Boxes of Stolen Hot Wheels After Colton Train Heist

A California train burglary ended with a punchline this week — and $54,000 worth of toy cars back in police hands. Officers in Colton arrested a man early Thursday morning after catching him loading boxes of Hot Wheels from a freight train into a pickup truck, a case that shows how organized cargo theft has become — and why the stolen goods often end up for sale online, where unsuspecting buyers can get pulled into the crime.

The 3 A.M. Call That Derailed a Train Heist in Colton

It started around 3 a.m. on Thursday, October 22, 2026, when a 911 caller reported that thieves were robbing trains near the end of Maple Street in Colton, California, a city in San Bernardino County's Inland Empire. "Yeah, they're robbing the trains down here at the end of Maple Street," the caller said in audio the department later posted on its Facebook page.

A Colton Police Department officer positioned himself near South 7th Street and South La Cadena Drive, close enough to hear the theft in progress. "I can hear them loading up some boxes right now," he said on bodycam audio while waiting under a nearby bridge. When a black Chevrolet Silverado pickup truck pulled away, the officer raced back to his patrol car, followed it, and pulled it over moments later. The driver stepped out with his hands on his head and was taken into custody without incident.

350 Boxes of Hot Wheels Worth $54,000 — and Three Charges

Inside the truck, police found 350 boxes of Hot Wheels cars, each box containing multiple vehicles, stolen from the freight train. Investigators valued the merchandise at approximately $54,000. The suspect was booked into the West Valley Detention Center on suspicion of burglary, possession of stolen property, and grand theft — California Penal Code sections 459, 496(a), and 487. Police have not released the suspect's identity, and as with any arrest, the charges are allegations that have not been proven in court.

The department celebrated the bust online with a pair of puns, writing "We derailed his plans!" alongside photos of the recovered boxes, and closing with, "His wheels weren't hot enough to get away!" The department also posted bodycam video and the 911 audio, crediting the early tip for giving officers time to act. "To have an arrest of that extremity, it's a big deal," a department spokesperson said.

Why Train Cargo Theft Is Booming in the Inland Empire

This was not an isolated incident. Residents living near the tracks off Maple Street told reporters the area is a recurring hotspot for train theft, though some were scared to speak on camera for fear of retaliation. Earlier in October, a group of thieves led police on a high-speed chase before dumping their car in Crestline and escaping on foot. Freight trains are attractive targets because they sit for long stretches in rail yards and along sidings, often carrying mixed cargo that is easy to grab and hard to trace — and a single box of collectible toys can be worth far more on the secondary market than its shelf price suggests.

Hot Wheels are a perfect example. What looks like a children's toy is also a serious collector's market, where rare castings, limited runs, and sealed cases command real money. Thieves know this. A truckload of sealed boxes is not a prank haul — it is inventory, and investigators say they are still tracking where these toys were headed for resale.

Where Stolen Collectibles Go: the Resale Pipeline Buyers Should Watch

Stolen merchandise rarely stays stolen for long. It gets fenced — sold quickly, often online, through marketplace listings, auction sites, and social media sales groups where a seller can move volume without ever meeting a buyer in person. Collectibles are ideal for this because buyers expect to see sealed cases, bulk lots, and "warehouse find" listings, and because a toy car has no serial number a buyer can check against a stolen-property database.

That creates a second victim pool: ordinary collectors and parents who buy what looks like a bargain and end up holding stolen property. In many states, knowingly buying stolen goods is itself a crime, and even an innocent buyer can lose the item — and the money — when police trace it back. If a deal looks impossibly good, there is often a reason.

How to Spot a Deal That's Too Good to Be True

Before you buy collectibles — or any high-demand goods — from an unfamiliar seller, run through a few checks:

Price-check the seller, not just the item. If sealed cases or bulk lots are listed far below every other seller's price, ask why. Legitimate sellers rarely undercut the whole market by half.

Look for a real history. A seller with no reviews, a brand-new account, or a profile that appeared days ago and is suddenly moving large quantities of one product is a red flag — especially for sealed, new-in-box merchandise.

Be wary of vague sourcing stories. "Warehouse liquidation," "estate sale," and "bulk overstock" are the classic cover stories for fenced goods. A legitimate reseller can usually say where the inventory came from.

Pay through protected channels. Marketplace checkout systems and payment platforms with buyer protection give you recourse if an item turns out to be stolen or never arrives. Wire transfers, gift cards, and peer-to-peer payments with no purchase protection do not.

Report suspicious listings. If you spot bulk sealed merchandise at impossible prices from a seller with no track record, report the listing to the platform — and if you believe you already bought stolen goods, contact local law enforcement rather than trying to resell them yourself.

The Colton case is still under investigation, and police have not said where the Hot Wheels were headed. But the lesson travels well beyond one rail yard: when cargo theft meets online resale, the bargain hunter is the last stop on the fence's supply chain — and the one left holding the bag.


Florida Man Steals a Dead Man's Identity to Take Over His House

A deed under scrutiny 

A South Florida police officer has been arrested on felony charges after investigators say he spent four years using a dead man's name, Social Security number, and house as his own — a scheme that began, detectives allege, on the very day he helped discover the man's body. The case is a textbook example of deceased identity theft, and it shows why the identity of someone who has died needs protecting just as much as the identity of someone still living.

The 2022 Welfare Check Where Officer Brian Sguros Found Dennis West Dead

On July 11, 2022, Brian Sguros, an officer with the Lauderhill Police Department in Broward County, Florida, responded as a backup officer to a welfare check at a home on N.W. 12th Street in Lauderhill. A neighbor had called 911 after not seeing the homeowner, 71-year-old Dennis West, for more than a week. West was found dead inside the front entrance of his home, and the medical examiner ruled that he died of natural causes from cardiovascular disease.

According to the Broward Sheriff's Office, Sguros inserted himself into West's affairs almost immediately. Investigators say he represented himself to the Broward County Medical Examiner's Office as West's friend and stated that West had no living family — claims detectives say were false, with no indication the two men ever knew each other. He even offered to arrange a funeral service if no family members were located.

How the Alleged Scheme Kept Dennis West "Alive" on Paper for Four Years

Detectives describe what followed as a complex, years-long identity theft and property fraud scheme. In a sworn filing, Sguros acknowledged taking possession of West's house on August 1, 2022 — less than a month after the welfare check — without any legal authority to do so. From there, investigators allege, he worked to make it appear that West was still alive:

He paid the home's property taxes and utility bills in West's name for years. He allegedly forged West's signature on a City of Lauderhill building-permit application — investigators say he also used a notary's name and seal on the application — and sent documents from his own cellphone. And on multiple occasions, he allegedly accessed law enforcement databases to pull information about West, which the arrest affidavit says included West's address, date of birth, and Social Security number.

Meanwhile, he renovated. Sguros told investigators he spent at least $214,000 of his own money over roughly two and a half years cleaning and repairing the deteriorating home, raising its value to approximately $500,000. His explanation, per the affidavit, was that he did it to protect the property from squatters and criminal activity. In February 2025, he filed paperwork with the Broward County Property Appraiser's Office claiming his possession of the property dated back to August 2022.

How It Fell Apart: the Heirs, the Lawsuit, and the October 20 Arrest

The alleged scheme surfaced when West's actual relatives — the living family Sguros allegedly said did not exist — sold the house to a real estate group in 2025, and a related civil case put his possession of the home in writing. According to the New York Post, Sguros went so far as to sue West's heirs seeking reimbursement for the renovations. A complaint in May of this year triggered a joint investigation by the Broward Sheriff's Office and the Property Appraiser's Crimes Against Property Unit, documented in a 21-page arrest affidavit.

Sguros was relieved of duty and placed on paid administrative leave on July 22 while the department investigated. He was arrested on Tuesday, October 20, 2026, and now faces five felony charges: official misconduct, criminal use of a deceased person's personal identification, criminal use of personal identification information, offense against a computer user, and unlawful use of a two-way communication device. After the arrest he was placed on leave without pay; he appeared in court the following day and was later released on bond. As with any criminal case, the charges are allegations that have not been proven in court, and the investigation remains ongoing.

What Is Deceased Identity Theft — and Why This Case Fits the Pattern

Deceased identity theft, sometimes called "ghosting," is the use of a dead person's personal information — name, date of birth, Social Security number — to open accounts, file paperwork, claim property, or make the person appear alive on paper. The dead are attractive targets for a simple reason: nobody is watching. There is no victim checking statements, no credit monitoring alerting anyone, and there is often a gap between a death and the moment banks, agencies, and credit bureaus update their records. A vacant house makes it worse, because an empty property with a deceased owner can sit unnoticed for years while mail, tax bills, and utility accounts keep flowing in the dead person's name.

This case allegedly adds the most dangerous ingredient of all: insider access. Investigators say the personal data came from law-enforcement databases, and the "still alive" illusion was maintained through exactly the routine paperwork — taxes paid, utilities on, permits pulled — that normally signals a legitimate owner. That is what makes deceased identity theft so hard to spot from the outside.

How Families Can Protect a Loved One's Identity After a Death

If you are settling a loved one's affairs, treat their identity like an asset that still needs guarding:

Notify the key agencies promptly. Report the death to the Social Security Administration, and send certified copies of the death certificate to the person's banks, creditors, and the three major credit bureaus, asking each bureau to flag the file as deceased so nothing new can be opened in their name.

Watch the mail and the property. Statements, tax documents, or new-account letters arriving in a deceased person's name are red flags. If the home will sit empty, visit it or have someone check on it, keep the mail secure, and periodically search the county property appraiser and clerk records for filings, permits, or transfers you did not authorize — in this case, a property filing was allegedly made years after the owner's death.

Be skeptical of "friends" who appear after a death. Anyone who volunteers to handle a deceased person's affairs, claims the person had no family, or discourages relatives from getting involved should be verified independently — especially if they work in a job that gives them access to personal records.

Report suspected fraud. Identity theft involving a deceased person can be reported at IdentityTheft.gov and to local law enforcement; the IRS also has a process for flagging a deceased taxpayer's account to block fraudulent returns.

West's story is a reminder that identity theft does not end at death — and that for four years, on paper at least, Dennis West appeared to be paying his taxes, keeping his lights on, and fixing up his house. Investigators say the man doing it was the officer who found him.

Thieves Stole $963,000 in Trading Cards From a FedEx Truck — Now the Stolen Cards Could Turn Up For Sale


FedEx trucks; CC BY-2.0 Wikimedia Commons
 

A parked delivery truck, a broken lock, and about an hour of nobody watching. That is all it took for thieves to pull off one of the biggest trading card theft jobs in recent memory — and if you buy collectible cards online, the fallout from this heist could land in your shopping cart.

What Happened Outside PSA Headquarters in Santa Ana

On October 13, a FedEx truck loaded with graded trading cards was parked outside the headquarters of Professional Sports Authenticator — better known as PSA — in Santa Ana, California, about 33 miles southeast of Los Angeles. PSA is the company collectors pay to authenticate cards, grade their condition, and seal them with a certificate number.

According to the Santa Ana Police Department, the driver left the truck unattended for somewhere between 60 and 90 minutes. When the truck was checked again, the lock was gone. Two full pallets of packages had been stolen — roughly 100 packages per pallet — and a third pallet holding about 50 more packages had been disturbed. All told, around 250 packages of cards disappeared.

Police put the estimated value of the stolen cards at $963,000, while noting the exact total has not been determined yet and the value of the third pallet was still being assessed. The cards were a mix of sports cards and Pokémon cards that had finished the grading process and were being shipped back to the collectors who own them. As of October 20, police had made no arrests and recovered none of the stolen items.

Why Graded Cards Have Become a Prime Target for Cargo Theft

Trading cards are not a kids' hobby anymore. They are an investment market, and professionally graded cards in sealed holders can sell for many times what an ungraded copy brings. Rare cards have sold for millions of dollars, which makes a pallet of freshly graded cards worth stealing in a way a pallet of toys never would be.

This kind of cargo theft is attractive to criminals for another reason: cards are small, light, untraceable at a glance, and easy to move through online marketplaces, card shows, and social media sales groups. Two pallets can fit in a single vehicle and be scattered across a dozen selling accounts within days.

The human cost sits with collectors like Skyler Bennett, who posts as Sky-B Cards on YouTube. Bennett told reporters that 104 of his cards were in the stolen shipment — cards he had spent two years accumulating and paid more than $8,000 to have graded. His order alone was insured for up to $156,000, and he said many of the cards are irreplaceable.

PSA Deactivated the Certificates on the Stolen Cards

There is one piece of good news for buyers. Collectors, the parent company of PSA, says it has deactivated the certificates for every card in the stolen shipment and notified its marketplace partners to watch for rare and serialized items turning up for sale. Each genuine PSA graded card carries a unique certification number, and a deactivated number is a red flag that the card in the holder is part of this theft.

Collectors also said it contacted affected customers directly and arranged compensation based on fair market value, and both the company and FedEx say they are working with law enforcement. FedEx called shipment security a top priority in its statement.

The Scam Risk: Stolen Cards and Fake PSA Emails

Here is where this story turns into a fraud warning. Nearly a million dollars in stolen merchandise has to be sold somewhere, and the most likely venues are the same places honest collectors shop: online marketplaces, auction sites, livestream sales, and buy-and-sell groups. Expect some of these cards to surface with prices that look like bargains — because the seller's cost was zero.

There is a second risk. Customers affected by the theft have posted online about receiving emails from PSA explaining what happened. Whenever a company sends a mass email like that, scammers copy it. Fake messages pretending to be PSA, Collectors, or FedEx — asking victims to "verify their claim" or "confirm compensation" through a link — are exactly the kind of collectibles scams and phishing attempts that follow a public theft like this. If you were affected, go to the company's real website yourself instead of clicking links in any email.

How to Protect Yourself When Buying PSA Graded Cards

Before you pay for any high-value graded card, run its certification number through PSA's online cert verification tool. If the number comes back deactivated, invalid, or belonging to a different card than the one pictured, walk away — no matter how good the price looks.

Buy through established marketplaces with real buyer protection, and be suspicious of sellers who push you toward off-platform payments, gift cards, or wire transfers. A rare or one-of-one card offered well below its recent sales prices, by a brand-new account, with pressure to pay fast, is the classic shape of a scam. And keep your own records: if you submit cards for grading, photograph them and save the certificate numbers, so you can prove what is yours if a shipment ever goes missing.

Police in Santa Ana are still investigating, and the exact value of what was taken may climb past the $963,000 estimate once every pallet is accounted for. Until the cards are recovered, the safest assumption for collectors is simple: the stolen inventory is out there, it will be offered for sale, and the certificate check takes thirty seconds. Do it every time.

Trucking Company Owner Pleads Guilty to 18 Counts in $2.1 Million Credit Card Bust-Out Fraud: How the Scheme Worked

A trucking company pleads guilty to a credit card bust out fraud.

credit: Igor Passchier

A California trucking company owner is facing federal prison after admitting he built a $2.1 million fraud machine out of other people's identities. On October 15, 2026, Hasan Korkmaz, 45, of Las Vegas, pleaded guilty in federal court to all 18 counts of an indictment charging him with bank fraud, money laundering, and aggravated identity theft.

Korkmaz owned and operated San Diego Logistics Group Inc., a trucking company based in Santee, California. Prosecutors say he used it as both cover and cash register for a credit card fraud operation that ran through 2022 and 2023. Here is how the scheme worked, and what it teaches the rest of us about protecting our own identities.

What Is a Credit Card "Bust-Out" Scheme?

A bust out scheme is one of the oldest tricks in financial fraud, and one of the most damaging. The fraudster opens credit card accounts that look completely legitimate, sometimes even making small on-time payments to build up the credit line. Then comes the "bust out": the cards are maxed out all at once, with no intention of ever paying the balance.

According to the Department of Justice, Korkmaz's version started with identity theft. He obtained names, dates of birth, Social Security numbers, and other personal information belonging to real people. Using those stolen identities, he applied for numerous credit card accounts in their names.

Once the cards were open, he ran up charges in the thousands of dollars each, including single transactions as high as $18,500, at various businesses, including his own San Diego Logistics Group. Charging his own company was a key move: it funneled the banks' money directly into a business he controlled.

The Bad-Check Trick That Kept It Going

What made this scheme run for two years was a second layer of fraud. To keep the cards alive, Korkmaz made payments on the accounts using checks drawn on accounts with insufficient funds, or drawn on accounts that did not exist at all.

These phantom payments temporarily restored the cards' available credit limits, because banks typically credit a payment before the check actually clears. Korkmaz would then immediately max the cards out again before the bad checks bounced. Each cycle extracted more of the banks' money, and each bounced check was just the cost of doing criminal business.

In total, prosecutors say Korkmaz caused more than $2,103,000 in losses to two banks. He also admitted to laundering the proceeds internationally, transferring funds to a bank account in Türkiye that he controlled.

The 18 Counts He Admitted

Korkmaz pleaded guilty to 12 counts of bank fraud, two counts of money laundering, and four counts of aggravated identity theft. The aggravated identity theft charges are particularly serious: each carries a mandatory minimum prison sentence that must run consecutively to any other sentence, meaning they stack on top of the bank fraud punishment rather than running at the same time.

His trucking company, which federal records show specialized in hauling refrigerated meat and fresh produce with three tractors and five drivers, now has an inactive federal motor carrier registration. The business that served as the scheme's front is effectively finished.

How to Tell If Your Identity Is Being Used in a Bust-Out

The most unsettling part of this case is that the victims were real people whose information was used to open cards they never knew existed. Bust-out schemes depend on victims not noticing. Here is how to catch it early:

Check your credit reports regularly. You are entitled to free weekly reports from all three bureaus at AnnualCreditReport.com. Look for accounts you did not open, inquiries from lenders you never contacted, and addresses you never lived at. Any of these can signal someone is building a bust-out in your name.

Freeze your credit. A freeze is free, takes minutes, and blocks new accounts from being opened in your name. You can temporarily lift it when you legitimately apply for credit. There is almost no reason not to have one in place.

Watch for small strange activity. Fraudsters sometimes test stolen identities with small transactions before the big bust-out. A charge you do not recognize, even a tiny one, deserves a call to the card issuer.

Guard your Social Security number. Korkmaz needed real SSNs paired with real names and birth dates. Shred sensitive mail, be skeptical of anyone who asks for your SSN outside of clearly legitimate contexts, and assume any data breach involving your SSN means you should be monitoring your credit closely.

Red Flags for Business Owners

This case also carries a warning for merchants. A customer repeatedly running large charges through your own business, especially round-number or near-limit transactions, followed by payments that later bounce, is a classic fraud prevention red flag. Payment processors and banks watch for this pattern, and it was part of what brought Korkmaz down.

If you run a business, reconcile your merchant account activity against actual goods and services delivered, and treat repeated large card-not-present or keyed-in transactions from the same source with extra scrutiny.

The Bottom Line

Hasan Korkmaz turned stolen identities into a $2.1 million pipeline, and the banks, and ultimately their customers, paid for it. His guilty plea on all 18 counts shows how seriously federal prosecutors treat bust-out schemes, which combine identity theft, bank fraud, and money laundering into a single operation.

For the rest of us, the defense is unglamorous but effective: freeze your credit, read your credit reports, and treat your Social Security number like the master key that it is. The victims in this case did nothing wrong. They just did not know someone else was spending in their name until the FBI came calling.

LA Bar Group Turned a $60,000 Dodgers Bet Into a Playoff Hedge — and Why Scammers Love Stories Like This


Some restaurants are turning to a Kalshi bet and they actually won.

credit: Courtney Garner

An LA restaurant group just turned heartbreak into profit. After the Los Angeles Dodgers failed to reach the World Series, a hospitality group operating 25 bars near Dodger Stadium revealed it had placed a $60,000 trade on the Kalshi prediction market betting the team would not advance. The position returned nearly twice the original stake, softening the blow of the playoff revenue those bars never got.

It is a clever piece of financial engineering, and a completely legitimate one. But stories like this are exactly what scammers love most, because they make an exotic-sounding financial move look easy, repeatable, and risk-free. Here is what really happened, how prediction markets work, and the scams this headline could inspire.

What the Restaurant Group Actually Did

According to Reuters, which reported the story on October 16, 2026, the group bought contracts on Kalshi paying out if the Dodgers failed to advance in the playoffs. When the team was eliminated, the trade settled in their favor at nearly double the $60,000 stake, returning roughly $120,000.

This is a textbook hedge. The bars' business depends heavily on game-day crowds, and a deep Dodgers playoff run means packed houses for weeks. If the team advances, the bars make their money the normal way and the $60,000 hedge expires worthless. If the team gets knocked out, the payout offsets the lost revenue. Either way, the business smooths out a risk it cannot control. It is the same logic as a farmer buying crop insurance, just applied to baseball.

Reuters noted the trade points to a small but growing use of prediction markets by businesses seeking protection against risks that conventional financial products do not cover. No standard insurance policy pays out when your local team loses.

How Kalshi Prediction Markets Work

Kalshi is a federally regulated exchange where users trade binary contracts on real-world outcomes: elections, sports results, economic data, entertainment events. Each contract pays $1 if the outcome happens and $0 if it does not, and the price in between reflects the market's estimated probability.

That regulatory status matters. Kalshi operates under the oversight of the Commodity Futures Trading Commission, which distinguishes it from offshore sports betting sites and unlicensed crypto casinos. Your money sits with a regulated US exchange, not a website registered in a jurisdiction you cannot find on a map.

Why Scammers Love Stories Like This

Here is where the scam angle comes in. Every time a legitimate "someone made money with an unusual financial product" story goes viral, fraudsters build pitches around it. Expect to see versions of these soon:

Fake prediction-market platforms. Scammers clone the look of sites like Kalshi and advertise them through social media and messaging apps, promising the same kind of "hedge your business" trades. You deposit funds, see convincing fake gains on a dashboard, and discover the withdrawal button does nothing when you try to cash out. The platform was never real.

"Guaranteed hedge" signal sellers. Fraudsters sell subscriptions to "expert" picks framed as risk-free hedges, borrowing the language of the Dodgers story. They show screenshots of winning trades and testimonials, never mentioning the losing ones. Real hedging involves real risk and real math; anyone selling certainty is selling something else.

Impersonation of the real thing. Scammers impersonate employees of legitimate exchanges, contacting small business owners with "exclusive hedging programs." The real Kalshi does not cold-message bar owners on WhatsApp offering managed accounts.

Recovery scams. After victims lose money to any of the above, a second wave of scammers arrives offering to recover the funds for an upfront fee. They recover nothing.

How to Tell a Real Hedge From a Scam Pitch

The Dodgers trade worked because the group understood exactly what it was buying: a defined payout on a defined outcome, sized against a real business risk. Ask these questions before touching anything that sounds similar:

Is the platform regulated, and can you verify it independently? Do not trust a badge on the website. Check the regulator's own registry. Is anyone promising returns or calling it risk-free? A hedge reduces risk; it does not eliminate it, and the $60,000 stake in this story could easily have gone to zero. Are you being rushed? Legitimate exchanges do not run countdown timers on "exclusive" opportunities. And are you being contacted out of the blue? Real financial platforms do not prospect for clients through direct messages.

The Bottom Line on Sports Betting Scams

The LA group's trade was smart, legal, and fully disclosed through a regulated market. It deserves credit as creative risk management. But its viral appeal, big number, famous team, clever twist, is precisely the formula scammers use to dress up investment scams and gambling scams as financial sophistication.

If a story makes a complicated money move look effortless, assume someone dishonest is already writing the pitch deck. Enjoy the ingenuity of the real trade, and keep your $60,000 far away from anyone who promises you can do the same thing with none of the risk.

Former UAH Employee Accused of Stealing $600K From University Foundation With Fake Invoices

UAH Shelby Center on the University of Alabama in Huntsville campus

Photo via Wikimedia Commons (CC BY-SA 2.0)

A 51-year-old former employee of the University of Alabama in Huntsville is facing a Class A felony charge after investigators say he allegedly stole roughly $609,598 from the UAH Foundation using counterfeit invoices.

Michael Paul Julius Benfield, 51, of Madison, Alabama, was arrested in September 2026 and charged with aggravated theft by deception, a Class A felony because the alleged amount exceeds $200,000. Court records say the alleged scheme ran from October 2023 through August 2026, with Benfield allegedly creating fake invoices that reimbursed him directly to his personal account.

A UAH police investigator swore out the arrest warrant on Sept. 9, and a university internal auditor is a key witness for the state. Benfield was booked into the Madison County Jail and later released on a $5,000 appearance bond. The university says he is no longer employed, that it notified law enforcement as soon as the alleged misconduct was discovered, and that the investigation is ongoing. His former role was Deputy Director for the Center for Modeling, Simulation, and Analysis, and his university staff webpage has since been removed.

How fake-invoice schemes work

Cases like this are a textbook example of invoice fraud, sometimes described as vendor fraud or internal embezzlement. The method is simple: a trusted insider creates bogus invoices that look routine, pushes them through the organization's payment system, and pockets the reimbursements. Because the payments appear to be ordinary expenses, they can go unnoticed by busy finance offices for months or even years.

Red flags and how organizations can fight back

This case is a fraud alert for any organization that pays vendors or processes reimbursements. A university scam of this kind can quietly drain hundreds of thousands of dollars before anyone spots it. Experts recommend a few basic defenses:

  • Independently verify any new vendor or changed bank details before money goes out.
  • Require dual approval on payments and reimbursements above a set dollar threshold.
  • Separate duties so the person who submits or creates an invoice cannot also approve it.
  • Run regular independent audits, and review recurring reimbursements to the same recipient.

Remember: Benfield is accused and charged, not convicted — everyone is innocent until proven guilty. We will keep following this crime news story as the case moves through the courts.

Tech CEO Arrested on Federal Charges for Allegedly Smuggling $300M in Nvidia AI Servers to China

Computer server racks

Photo via Techicy

In October 2026, the owner of a Southern California technology firm was arrested on federal charges accusing him of smuggling more than $300 million in computer servers restricted by U.S. export controls to China, according to the U.S. Department of Justice.

The Arrest

Greg Lui, 38, who also goes by "Yiu Kong Lui" and lives in San Gabriel, California, was taken into custody under a three-count federal indictment handed down by a grand jury on September 29. Lui is the owner of Earthmade Computer Inc., a technology company based in the City of Industry. He made his initial court appearance and was arraigned on October 1 in federal court in downtown Los Angeles.

How the Alleged Scheme Worked

Prosecutors allege that from 2023 to 2024, Lui and his co-conspirators used Earthmade to purchase high-end computer servers loaded with U.S.-made graphics processors (GPUs) built for advanced computing work — including Nvidia A100 and H100 chips, according to reports. U.S. law bars the sale of these chips to China without a special license.

Rather than applying for licenses, Lui allegedly filed false paperwork with U.S. manufacturers claiming the equipment was bound for buyers in Malaysia or Singapore — countries where no such license is required. From there, prosecutors say, the servers were quietly re-routed to buyers in China. Authorities allege the scheme even involved staged dummy servers meant to mislead inspectors and convoluted transshipment routes designed to hide the true destination.

In one example cited in the case, Lui allegedly submitted a purchase order in January 2024 for 27 servers worth about $7.6 million, shipped from Los Angeles County to Kuala Lumpur, Malaysia. Two months later, a co-conspirator allegedly told a Malaysian government official the shipment had already been forwarded to a Chinese customer. Between January and October 2024, Earthmade allegedly received more than $176 million from two Malaysia-based shipping companies tied to the scheme.

The Charges

Lui faces one count of conspiracy to violate the Export Control Reform Act and the Export Administration Regulations, one count of outbound smuggling, and one count of conspiracy to commit money laundering. If convicted on all counts, he could face a statutory maximum of 20 years in federal prison on the conspiracy count, 20 years on the money laundering count, and 10 years on the smuggling count. The case is being investigated by the FBI's Counterintelligence and Espionage Division, the Commerce Department's Bureau of Industry and Security Office of Export Enforcement, and the Defense Criminal Investigative Service.

Why It Matters

Federal officials say the advanced chips at the center of this alleged chip smuggling operation could significantly boost the military capabilities of other nations — which is why U.S. export controls restrict them. First Assistant U.S. Attorney Bill Essayli said the defendant allegedly used false paperwork and shipments through third countries to smuggle more than $300 million in export-controlled computer servers to China. The FBI said Lui allegedly sold the Chinese government hundreds of millions of dollars' worth of American technology in violation of U.S. export control laws.

It is important to remember that an indictment is merely an allegation, and every defendant is presumed innocent until proven guilty in a court of law.

Ex-CIA Official With Top Secret Clearance Pleads Guilty to $194 Million Fraud Involving 298 Gold Bars

Stacked gold bullion bars


Photo via Wikimedia Commons

The $194 Million Scheme

David J. Rush of Ashburn, Virginia, held senior executive posts and a top-secret TS/SCI security clearance at a federal agency court filings call "Government Agency 1." On October 6, 2026, he pleaded guilty in federal court in Alexandria, Virginia, to one count of wire fraud for siphoning roughly $194 million in government money through two invented classified programs. Under his plea agreement, he owes at least $195.4 million in restitution. CIA Director John Ratcliffe said the CIA referred the case to the FBI after its own internal investigation turned up potential crimes.

The first fake program was a bogus Special Access Program. Between November 2025 and March 2026, a government contractor wired about $145 million to Rush's shell company, 0701 Holdings LLC, for "consulting" that never happened. The second program had a subcontractor buying gold bars — 298 of them, costing $46,361,721 including fees — delivered in Pelican cases straight to Rush's government office in Loudoun County.

298 Gold Bars and Four Florida Mansions

On May 19, FBI agents searched Rush's home and found all 298 gold bars — plus about $2.1 million in cash, €104,795 in euros, and more than 30 watches, including Rolexes. The "consulting" millions, meanwhile, had been converted into South Florida luxury real estate: two Palm Beach homes at $21.9 million and $27 million, a $13.65 million Palm Beach parcel, and a $40 million parcel in Hobe Sound. He also billed the government $1.8 million for private charter flights. Total losses: $193.6 million.

The forfeiture list reads like a heist movie inventory: the gold, the cash, 35 watches, two 2026 BMW Alpina XB7s, $38.65 million seized from the shell company's bank account, and the Florida properties.

A Resume Built on Lies

Rush didn't just invent programs — he invented himself. Prosecutors say he landed his senior position partly by lying about his background: claiming to be a combat veteran and military pilot with degrees he never earned. He left the Navy reserves in 2015, yet claimed 392 hours of military leave starting in 2021. He also admitted handing a foreign government official information about a U.S. clandestine human source in late 2025 — a stunning breach on top of the fraud.

What Happens Next

Rush faces up to 20 years in federal prison, with sentencing set for January 28, 2027. Attorney General Todd Blanche vowed to keep rooting out waste, fraud, and abuse, the Director of National Intelligence has asked the Intelligence Community Inspector General to investigate, and the DOJ says its probe is continuing. The lesson for this October 2026 scam alert: the biggest cons don't always come from a phishing email — sometimes they come with a security clearance.

Huntsville Trafficking Suspect Arrested Again as New Victim Is Added to Meteor Buffet Case

Caiyun Chen mugshot over police lights background
Mugshot via Madison County Sheriff's Office

The Initial Charges (August 27, 2026)

On August 27, 2026, Huntsville police, the FBI, and several other agencies raided six locations — including the Meteor Buffet on Highway 72 East — in an operation dubbed Operation Meteor Strike. Three people were arrested and booked into the Madison County Jail: 51-year-old Caiyun Chen on first-degree human trafficking, 64-year-old restaurant owner Chao Bin Zhang on conspiracy to commit a crime, and 44-year-old Baudilio Ordonez-Gomez on conspiracy to commit a crime.

Investigators say the case began when a woman came forward saying she had been brought to Huntsville, Alabama and forced to work for roughly two years to pay off a debt, under threat of deportation.

How They Bonded Out

All three eventually got out. Zhang bonded out the Friday morning after his arrest. Chen, who initially had no bond set, was later released on a $100,000 bond. Ordonez-Gomez was held on a $30,000 bond. Zhang later waived his preliminary hearing on September 16, 2026, sending his case toward a grand jury.

The New Charges (October 2, 2026)

On Friday night, October 2, Huntsville police arrested Chen again — this time on a new first-degree human trafficking charge tied to an additional victim in the same case. No bond was set this time, and she remains in jail, according to a WAFF report published October 3, 2026.

All three defendants are presumed innocent. The charges are allegations, and none of the cases has gone to trial.

The Meteor Restaurant is at the Center of It All

Meteor Buffet is a Chinese buffet restaurant at 751 Highway 72 East in Huntsville. Like most buffets, it employed kitchen workers behind the scenes and servers and cashiers up front — and the labor-trafficking investigation has centered on how some of those workers were treated. Investigators say the victim in the case was forced to keep working to pay off a debt, a pattern known as debt bondage.

Meteor Buffet restaurant building in Huntsville, Alabama
Meteor Buffet, Huntsville, Alabama

The 2019 Crab-Legs Brawl

This is not the first time Meteor Buffet made headlines. In 2019, the restaurant went viral after a brawl broke out over crab legs: diners John Chapman and Chequita Jenkins were arrested after allegedly fighting with serving tongs like fencing swords while waiting in line. Huntsville police officer Gerald Johnson, who happened to be eating there, told WHNT that plates were shattering and “there’s a woman who’s beating a man.” Jenkins was charged with third-degree assault and Chapman with disorderly conduct.

Why This Matters for Scam Awareness

Labor trafficking cases often begin the way many scams do: false promises. Victims are lured with offers of steady work and decent pay, then find wages withheld, movements restricted, or documents taken. If a job offer demands your passport, charges fees just to start work, or refuses to put terms in writing — walk away. It is a textbook scam awareness lesson. This remains a developing crime news story from October 2026, and investigators say more charges are possible. Anyone with information about labor trafficking can contact the National Human Trafficking Hotline at 1-888-373-7888.

Alleged $126 Million Fake-Postage Scheme: How One Website Sold Millions of Bogus Shipping Labels

U.S. mailbox with flag

Photo via The Times of India

A federal case out of Florida is a fresh reminder of how online scams can quietly grow into enormous alleged losses. Prosecutors say 33-year-old Pakistani national Faheem Akram ran LabelsBank.com, a website investigators say was never authorized to sell official mailing products, and sold what they describe as counterfeit labels for a flat fee of about two dollars each — no matter a package’s weight, size, or destination.

A simple idea with a massive reach

According to court records, buyers used the allegedly fake postage to ship packages at far below legitimate rates, leaving the Postal Service to absorb the difference. Investigators estimate that more than 5,200 people bought over 5.1 million of the suspect labels, producing alleged losses to USPS of more than $126 million.

U.S. Attorney Jason Reding Quiñones for the Southern District of Florida described the alleged operation as simple but huge: sell bogus postage online at fixed bargain prices so customers could dodge legitimate mailing charges. Federal authorities have since shut the website down, seized the domain, and brought charges against the alleged operator, a Pakistani national.

$100,000 reward for information

Quiñones later announced on social media that the U.S. Postal Inspection Service is offering a reward of up to $100,000 for information leading to Akram’s arrest and conviction. Anyone with tips is asked to call postal inspectors at 1-877-876-2455 and say “Law Enforcement” — and officials stress that no one should attempt to apprehend the accused man themselves.

The charges the accused man faces

Akram is charged with one count of conspiracy to defraud the United States and to make and sell counterfeit postage stamps, five counts of making and selling counterfeit postage stamp labels, and four counts of wire fraud — a major postal fraud prosecution built on digital evidence. If convicted, he faces up to five years in prison on the conspiracy and counterfeit postage counts and up to 20 years on each wire fraud count.

Why email users should pay attention

Schemes like this one are often promoted through scam emails and phishing messages advertising impossibly cheap shipping supplies or linking to shady payment pages. Treat any unsolicited offer of discounted postage, gift cards, or delivery services as suspicious — legitimate carriers do not sell through random websites or email blasts.

Protecting yourself

Good fraud prevention starts with buying postage only through official carrier websites, apps, or retail locations, and never entering payment details on a site you reached through an unexpected message. Paying criminals for bogus labels can also expose buyers to identity theft, since these operations routinely harvest the financial information of everyone who checks out.

This prosecution is a reminder that cybercrime is not limited to inboxes and attachments — it thrives anywhere trust can be faked at scale. If a deal looks too good to be true, verify the seller through official channels before spending a dollar. (Based on reporting by The Times of India.)

Illinois Woman Loses $318K in Gold-Bar Scam, Then Helps Police Sting the Courier

Gold bars seized in the Marion Illinois scam case.
Photo via Capitol News Illinois

In a devastating example of an elderly scam, a 78-year-old woman from Marion, Illinois, was allegedly defrauded of hundreds of thousands of dollars in an elaborate gold-bar scam — and then helped investigators arrest the man accused of picking up the loot.

The Popup That Started It All

In April 2026, the woman — identified only as D.B. in federal court records — reportedly saw a pop-up on her computer warning that the machine had been compromised. She searched online for Microsoft support, called the first number shown in the results, and reached a man calling himself "Mike Williams." Williams allegedly claimed to be a supervisor on Microsoft's fraud-prevention team, and the woman gave him remote access to her computer.

An "Edward Jones" Impersonator Tightens the Grip

Williams then handed her off to another man calling himself "Kevin Jones," who claimed to work in Edward Jones' fraud-prevention department. Jones allegedly told her that her Edward Jones investment accounts had been compromised. The impersonation scheme quickly turned controlling: according to court records, Jones had her sign a purported nondisclosure agreement, send him "good morning" and "good night" texts every day, and carry a "tracker phone" that he monitored.

Nearly $1.8 Million Moved, Hundreds of Thousands in Gold

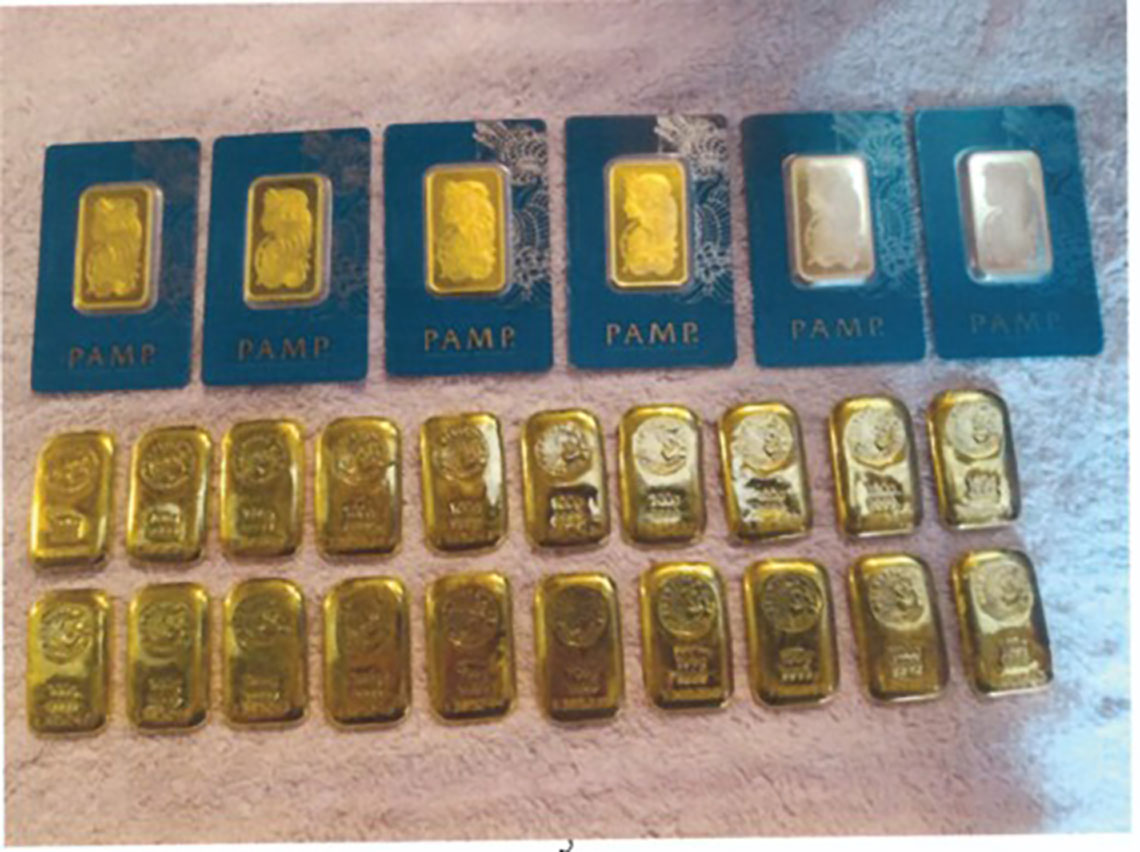
Following Jones's directions, she moved nearly $1.8 million from her Edward Jones accounts into a money market account and spent more than $823,000 on gold bars — purchases she believed were needed so a supposed federal agent could hold the gold for safekeeping. On June 8, she handed over gold worth $318,459 — six 1-ounce bars and twenty 100-gram bars — in the Marion Walmart parking lot to a man she believed was a U.S. Treasury agent, after exchanging the code word "black bug." Jones then told her to convert more than half a million dollars more into gold — and she did.

Doubts, Then a Call to Marion Police

She grew suspicious when the federal seal on documents Jones sent her did not look genuine, and she contacted the Marion Police Department.

The Sting: Sandbags and "Poker Queen"

Working with investigators, police helped arrange a sting. On July 7, Jones guided her to package two kilograms of gold bars worth about $272,000 and meet the supposed "agent" at the Cornerstone Church in Marion, near Sam's Club, using the code word "poker queen." The box was actually filled with sandbags. Investigators arrested Ruoyu Lian, 30, of Flushing, New York, moments after he took the box.

Guilty Plea and an Expected Prison Sentence

Lian pleaded guilty in federal court in Benton on September 24 to felony wire fraud and conspiracy to commit the same offense — each charge carrying up to 20 years in prison and a $250,000 fine. As of October 2026, he remains in the Franklin County Jail pending a January 14 sentencing hearing. Under the plea deal, his sentence is expected to fall within the federal guideline range of 40 to 52 months, and he will owe more than $318,000 in restitution for the gold that was never recovered. As a Chinese citizen and legal permanent resident, he is expected to be deported after serving his sentence. His defense attorney said Lian acted only as the scheme's "courier" — a New York sushi chef allegedly paid about two weeks' restaurant wages to fly to Illinois — and called him "expendable" to the ringleaders, who remain at large.

Federal Warning on Courier Scams

The FBI warned in September 2025 about a rise in so-called "gold bar and bulk cash courier scams," reporting more than 1,700 such scams between 2023 and May 2025 with reported losses exceeding $186 million.

Scam-Awareness Takeaways

Take this case as a scam alert. Red flags here included fake computer popups, a stranger gaining remote access to a computer, demands for secrecy and a purported NDA, and instructions to convert savings into gold for supposed "agents." No legitimate company or government agency operates this way — real tech support will never ask for remote access out of the blue, and real federal agents will never ask you to buy gold bars.

84-Year-Old Loses $30K in Fake FBI and Citibank Scam, Then Helps Police Catch the Pickup Man

Mugshot of Han Bing Wu.
Photo via Long Island Guide / Nassau County Police

An 84-year-old woman in Manorhaven, New York, was allegedly targeted in a cruel elderly scam — an impersonation scam in which callers posed as Citibank's fraud department and the FBI. She lost $30,000 — then helped detectives arrest the man accused of coming back for more.

A Fake Bank Alert and a Demand for Cash

On September 13, 2026, the woman reportedly saw what appeared to be a security alert on her computer from Citibank's fraud department. She called the number shown and was allegedly told to withdraw $30,000 in cash — and that an FBI agent would meet her to collect it.

$30,000 Handed to a Stranger

She withdrew the cash and handed $30,000 to an unknown man who met with her, according to Nassau County police detectives. She later realized she had been scammed and contacted police.

The Suspect Returns — and Police Are Waiting

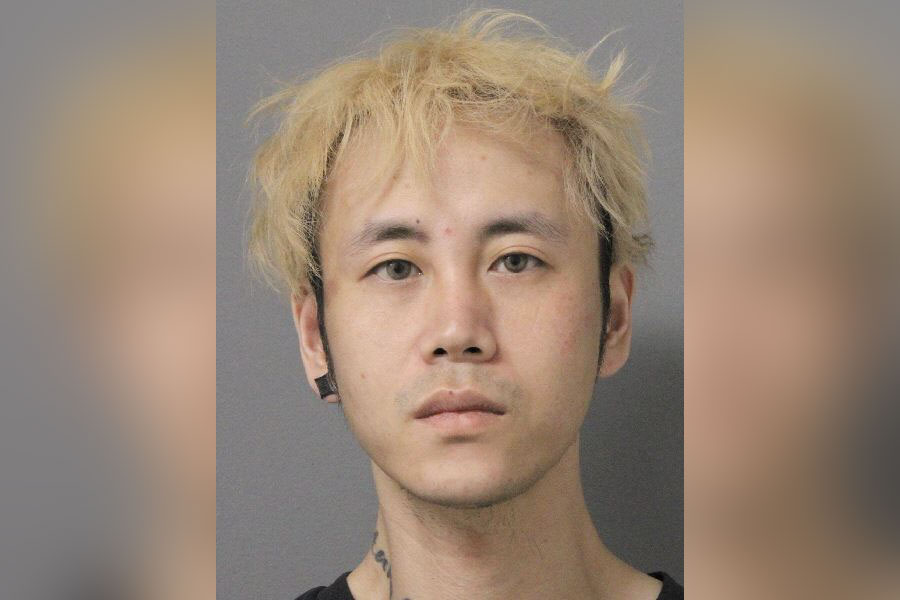
On September 17, she was contacted again and asked for another $18,000. This time she alerted detectives, who were in place when Han Bing Wu, 31, of Flushing allegedly arrived in Manorhaven to collect the money. He was arrested without incident.

A Different Man — and an Alleged Drug Find

Police emphasized that Wu was NOT the same man who collected the original $30,000. Wu was also allegedly found in possession of a substance police believe was ketamine.

Charges and the Ongoing Investigation

Wu was charged with attempted grand larceny in the third degree and criminal possession of a controlled substance in the seventh degree. He was scheduled for arraignment on September 18 at First District Court in Hempstead. The investigation remains ongoing, and Nassau County detectives ask anyone who believes they may have been victimized to contact the Sixth Squad at 516-573-6653.

Charges are accusations, and the defendant is presumed innocent until proven guilty.

Scam-Awareness Takeaways

Consider this a scam alert as of October 2026: beware popups claiming to be your bank, anyone telling you to withdraw cash for an "agent," and any supposed official who wants to collect money in person. No real bank or the FBI will ever collect cash from you in person.

Man Arrested on $2.65M Bond After Tennessee Senior Lost $51K in Social Security Impersonation Scam

Police arresting a suspect
Photo via Motorbiscuit

An Atlanta man is being held in a Tennessee jail on a $2.65 million bond after investigators say he acted as a courier collecting cash from an elderly victim in an elaborate scam that cost the senior more than $51,000.

How the Scam Worked

According to the Cumberland County Sheriff's Office, the victim received a call from someone claiming to be a federal agent with the Social Security Administration. The caller allegedly told the senior that his Social Security number had been compromised, his computer had been hacked, and even an employee at his own bank was secretly helping the cybercriminals. It was a textbook phone scam designed to spark panic.

Investigators say the scammer then talked the victim into buying a new laptop, granting the caller remote access to it, and withdrawing large amounts of cash to hand over to a visiting “courier” — supposedly for safekeeping until a secure account could be set up. Detectives described the scheme as a Social Security scam built on impersonation scam tactics.

Two Cash Handoffs Before the Arrest

Before realizing it was a scam, the victim allegedly made two massive cash handoffs to couriers:

  • September 22: $24,000 handed over at a Walmart in Cleveland, Tennessee
  • September 23: $27,000 handed over at a motel in Crossville, Tennessee

When the scammers demanded another $14,000, sheriff's investigators stepped in. Working with the victim and the Tennessee Bureau of Investigation's Cybercrimes unit, deputies arranged another meetup at a McDonald's on Peavine Road in Crossville with a decoy package. Abu Saleh, 47, of Atlanta, Georgia, was taken into custody on September 30 in the parking lot as soon as he collected the package, authorities said — an arrest that ended the alleged cash-pickup run.

The Charges and Bond

Saleh was booked into the Cumberland County jail on the following charges:

  • Theft of property over $10,000 ($300,000 bond)
  • Criminal attempt to commit theft of property over $10,000 ($150,000 bond)
  • Financial exploitation of an elderly person ($200,000 bond)
  • Fugitive from justice on an out-of-state warrant from Georgia ($2,000,000 bond)

Booking records identify Saleh as a citizen of Bangladesh and show an outstanding warrant from Atlanta, Georgia, involving a similar alleged cash pickup. U.S. Immigration and Customs Enforcement placed a detainer hold on him on October 1. He is scheduled to appear in Cumberland County General Sessions Court on Monday, October 5. The prosecution marks a significant elderly fraud case, and the October 2026 arrest underscores how aggressively such schemes target seniors.

Red Flags to Watch For

The Sheriff's Office urged residents to hang up immediately on anyone who tells them to withdraw cash, hand money to a courier, or grant remote computer access to “protect” their assets. Legitimate federal agencies never operate through cash pickups, never ask you to withdraw money for safekeeping, and never demand remote access to your computer. If you get a call like this, hang up and contact local law enforcement — and talk to a trusted family member before sending anyone money.

Two Suspects Caught With Nearly 700 Poached Ginseng Roots in Great Smoky Mountains National Park

Wild American ginseng roots
Photo via Shutterstock

Two people were recently stopped by Rangers in Great Smoky Mountains National Park while carrying hundreds of poached ginseng roots. The October 2026 wildlife crime case highlights how a profitable black market transforms a slow-maturing wild plant into a prime target for poachers — and how ordinary shoppers can end up financing the destruction without ever realizing it.

Two Individuals Digging for Smoky Mountain Ginseng

According to the National Park Service, rangers approached two different individuals for digging ginseng illegally inside the park, as shared in a park announcement dated September 30, 2026. One individual was found with 167 roots; the other carried 521 roots weighing about eight pounds — 688 roots combined. Because the law enforcement rangers acted quickly, many of the undamaged roots were recovered, and the park's natural resources team intends to replant them. Still, long-term records indicate that only roughly one-third of replanted ginseng survives, meaning most of the harm is irreversible.

Why Ginseng Gets Poached

Wild American ginseng is highly valued in traditional medicine, and that appetite sustains a booming illicit trade — published estimates put wild ginseng at up to $500 per dry pound. The species is exceptionally fragile: it takes seven to 10 years to mature and set seed, and individual plants can live past 75 years. Tearing hundreds of roots from the earth erases decades of growth in one afternoon, scars sensitive habitats, takes away food sources for wildlife, and weakens the plant's genetic diversity.

The Penalties Are Real

Gathering or even holding ginseng inside Great Smoky Mountains National Park is against the law. Those caught can face penalties of up to $5,000 in fines, up to six months of imprisonment, or both. Everything in the national park — animals, plants, even rocks — is under protection, and rangers pursue poaching cases aggressively.

How the Black Market Reaches Consumers

This is where the story turns into a consumer-fraud problem: poached ginseng doesn't remain in the forest. It moves through a shadowy supply chain where unlawfully dug roots are marketed as premium “wild” ginseng at marked-up prices. Buyers spending top dollar on products advertised as wild-harvested ginseng have little ability to check where the roots actually originated — and some of that merchandise was ripped from a national park. Any market that rewards “wild” sourcing with higher prices while providing almost no traceability sets up ideal conditions for fraud.

How to Not Fund Poaching

Park officials encourage shoppers to look closely at where ginseng products originate and to select sustainably grown ginseng instead of items purported to be wild-harvested. Treat bold “wild-harvested” claims with skepticism when sellers offer no evidence — particularly at premium prices. 

If you suspect poaching or unlawful harvesting within the park, report it to Great Smoky Mountains Dispatch at: 865-436-1230.

Florida Man Posed as Elon Musk and Scammed a Texas Woman Out of Nearly $600K

Jeffrey Moynihan scam

Jeffrey Moynihan was arrested after scamming a woman. (source: Bradenton Police Department)

A Florida man pretending to be one of the richest men in the world — Elon Musk — convinced a 74-year-old Texas woman he met on Facebook to hand him nearly $600,000, promising her an investment return of $56 million. Instead, he strung her along for months to earn her trust before taking her money. This is one of the most brazen investment scams built on celebrity impersonation in recent memory, and it carries lessons every internet user should know.

How the Elon Musk Impersonation Scam Worked

According to reporting by WAFF 48 News, the woman believed the man she met on Facebook was the real Elon Musk. After exchanging messages for months, she gave him almost $600,000 of her money because he promised to grow her investment into $56 million. The scammer played the long game: months of friendly conversation built the trust that made the massive "investment" feel safe. By the time the money was gone, there was no Musk and no investment — just a con artist in Florida.

The Man Behind the Fake Elon Musk

The man scamming her was Jeffrey Moynihan (seen in the image above), and he was arrested by the Bradenton Police Department, which serves the area on US 41 between Tampa and Sarasota, Florida. He pleaded "no contest" to the charges and received nearly 30 years of probation for his crimes. A representative of the department noted that scammers often target older people who may be more isolated: "A lot of times, people that are older may not have such a large social group. And if you're home alone for a day or two, and someone calls you or sends an email, and it's a very friendly email, it can really trick people." Hopefully his arrest is a wake-up call that ends his pattern of scamming honest people.

Red Flags in This Scam

  • A "celebrity" contacting you out of the blue. Real billionaires do not pitch investments to strangers on Facebook.
  • A promise of absurd returns: turning $600,000 into $56 million is fantasy, not finance.
  • Months of grooming: the scammer invested time in friendship before ever asking for money. Long cons are the hardest to spot.
  • No verifiable business, contract, or platform — just messages and promises.
  • Targeting isolation: the victim was 74 and home alone, exactly the profile scammers hunt for.

What to Do If a Stranger Contacts You on Facebook

If you think you are being targeted by a scammer, there are ways to protect yourself. First, stop all communication immediately. Next, alert a trusted family member, a friend, or a neighbor about what has been going on — tell them as many details as possible so they can help. Third, report the incident to your local police department, including the contact information for the individual.

And add these scam-proofing habits:

  • Never send money or "invest" based on a social media conversation, no matter how famous the person claims to be.
  • Verify identities independently: look for official, verified accounts and news coverage — not screenshots or links the stranger sends you.
  • Do a reverse image search on profile photos; scammers routinely steal pictures.
  • Report impersonation accounts to the platform and file a report with the FTC's ReportFraud.ftc.gov or the FBI's Internet Crime Complaint Center (IC3).
  • Talk about scams openly with older relatives — awareness is the best defense.

Celebrity impersonation scams only work when victims feel too embarrassed to ask for help. Jeffrey Moynihan got caught, but copycats are running this same playbook right now. If an "Elon Musk" slides into your messages with a can't-miss investment, delete it — the real one isn't looking for your money.

Mariam Ture $7.5 Million Inheritance Phishing Scam Email Exposed

Spam email warning graphic

Photo via Online Sciences

Did an email from someone calling herself "Mariam Ture" land in your inbox, offering you a share of a $7.5 million inheritance locked in a bank in the Ivory Coast? It's a scam — and a textbook example of an advance-fee fraud, one of the oldest tricks on the internet.

The "Mariam Ture" Scam Email, Explained

The message comes from a free Gmail address printed as mariamture (at) gmail.com — already a red flag, since no bank or law firm conducts business from a free email account. The email is written as an introductory message and follows a classic script. Here is the scammer's message, quoted verbatim so you can recognize it:

From Ms. Mariam Ture,

Please Reply me through my private email address for my security reason

( mariamture (at) gmail.com )

It is my pleasure to write you i decided to contact you to help me out of my problem, however is not mandatory nor will i in any manner compel you to honour against your will,but first Iet me introduce myself to you.

My name is Ms. Mariam Ture, Am 21 years of age, I am a student of high school before I lost my parents in a car accident last year, so I have been out from school and been looking for a sincere person that I will trust.

I am the only child of my late parents and that has made me to run away from our family house because my uncles are after my life to take away my inheritance which my late father left for me in a Bank here in Cote D'ivoire. My entire dream is to find somebody that I can trust with my future life and inheritance and also who will be able to invest it wisely in any lucrative business.

Nobody knows about the inheritance which worth $7.5 million dollars in Cash deposited in a Bank here with my name as the next of kin. And I want you to also keep it very confidential till we can be able to transfer this money from the Bank here to your country and I will fly to join you immediately for future plans of continue my education once a join you in your country.

I have to trust somebody to save my future and that is why I am trusting you now I want you to understand my critical situation and give me the assistance that I need so that I will have a better life and also enjoy my inheritance with you. I will tell you more about myself as soon as I hear back from you, your interest to assist me and also build more trust to be able to have a better understanding. Please Reply me through my private email address for my security reason ( mariamture (at) gmail.com )

I look forward for your urgent response, thank you and God bless you.

Best regard

Ms. Mariam Ture

Why This Is an Advance-Fee Scam: The Red Flags

  • It arrives out of nowhere from a total stranger. Real banks and estates do not email random people about inheritances.
  • The sob story: orphaned student, scheming uncles, a fortune she can't touch alone. Scammers manufacture emotional emergencies to short-circuit your judgment.
  • The secrecy demand: she insists you keep the inheritance "very confidential." Secrecy keeps victims from asking someone sensible for advice.
  • The free Gmail address and the plea to reply through her "private email" keep everything off the record.
  • The spelling and grammar errors are hallmarks of this genre — advance-fee (419) scams have used this same rough script for decades.
  • The "next of kin" hook is the setup: to "receive" the money you will eventually be asked for your bank account information — or for upfront fees. Whatever you do, do not hand over either.
  • The urgent tone and "God bless you" closing are trust bait. A little manufactured warmth makes the lie feel personal.

One correction worth noting: the Ivory Coast (Côte d'Ivoire) is in West Africa — not South Africa, as an earlier version of this warning stated.

What Happens If You Reply

If you respond to this first email, the scammer sends a follow-up message (that follow-up is covered in Part 2). The pattern is always the same: more story, more urgency, and eventually a request — pay a "transfer fee," cover "legal costs," or share your bank account information so the money can be sent. There is no $7.5 million. Anyone who pays or shares account details is the only one who loses money.

How to Protect Yourself

  • Don't reply. Any response tells the scammer your address is active.
  • Delete the message and mark it as spam or phishing in your email client.
  • Never send money, gift cards, or bank account information to someone who emailed you out of the blue.
  • Report email fraud to the appropriate authority in your country, such as the FTC's ReportFraud.ftc.gov in the United States.
  • Warn friends and family: this scam works because victims feel like the one person trusted with a secret.

If the "Mariam Ture" inheritance email found its way to you, now you know exactly what it is. Delete it and move on — and if you're reading this after replying, stop all contact immediately.

Email Phishing from Bedroom

Email Phishing from Bedroom